
How Small Businesses Can Go Sustainable

Sustainability is not just for large corporations. Small businesses can also make a big impact by adopting simple and practical changes. One of the easiest steps is reducing waste. This can include minimizing packaging, recycling materials, and avoiding unnecessary resource usage. Energy efficiency is another important area. Switching to LED lighting, using energy-efficient equipment, and […]

How Small Businesses Can Go Sustainable Read More »
AI-Powered Learning Platforms

Introduction: Smarter Learning Systems AI is transforming education by enabling intelligent learning systems. We see this as a major shift toward personalized and efficient learning experiences. Problem Statement Traditional learning methods fail to address individual student needs. Industry Insights AI platforms offer: Personalized learning paths Real-time feedback Performance tracking Strategic Solutions Implement AI-based platforms Use

AI-Powered Learning Platforms Read More »

Battery Power: India’s EV Backbone

Introduction: Batteries Decide the Game In the EV ecosystem, vehicles get the attention—but batteries control the economics. India’s 2047 vision will depend heavily on how effectively we build a self-reliant battery ecosystem. Market Gap Import dependency on lithium and components Limited battery recycling infrastructure High cost impacting EV affordability Strategic Focus Gigafactory development Battery-as-a-Service models

Battery Power: India’s EV Backbone Read More »

From Waste to Wealth: Reducing the Six Big Losses in Your Plant

Introduction In today’s competitive manufacturing environment, operational efficiency is essential for maintaining profitability, product quality, and customer satisfaction. One of the most effective ways to improve manufacturing performance is by identifying and eliminating waste. A proven framework for achieving this goal is addressing the Six Big Losses, a concept widely used in Total Productive Maintenance

From Waste to Wealth: Reducing the Six Big Losses in Your Plant Read More »

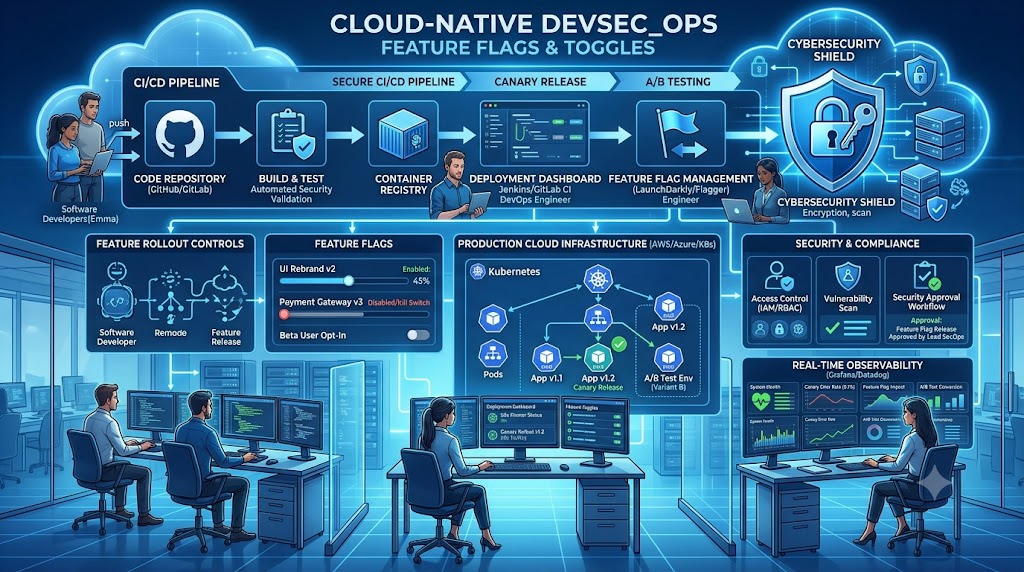
Security-First Feature Flags and Feature Toggles in Cloud-Native DevOps

Security-first feature flags and feature toggles are becoming an essential component of modern cloud-native DevOps environments. As organizations strive to accelerate software delivery while maintaining strong security standards, feature flags provide a powerful mechanism for controlling how and when new functionality is exposed to users. By separating deployment from release, teams can introduce features into

Security-First Feature Flags and Feature Toggles in Cloud-Native DevOps Read More »

Security‑First Compliance as Code in Cloud‑Native DevOps

In many organisations, compliance is treated as a separate, manual audit cycle: a checklist that’s checked once a year and then forgotten until next time. A security‑first “compliance‑as‑code” model flips this by embedding compliance rules into the same systems that ship software: every build, IaC change, and deployment is validated against living, versioned compliance policies

Security‑First Compliance as Code in Cloud‑Native DevOps Read More »

Security‑First Team Topologies in Cloud‑Native DevOps

In many organisations, security is an afterthought: teams are formed around features or clouds, and security is added as a separate function that must “engage” with them later. A security‑first team‑topology model builds security collaboration into the very shape of the organisation—embedding security minds into platform, product, and enablement teams so that secure choices are

Security‑First Team Topologies in Cloud‑Native DevOps Read More »

Security‑First Learning and Experimentation Culture in Cloud‑Native DevOps

In many organisations, experimentation happens in the shadows: engineers spin up unapproved clouds, unhardened clusters, or unmonitored APIs, and by the time security finds them, they’re already connected to production‑like data. A security‑first experimentation culture flips this by providing safe, well‑governed sandboxes where teams can explore new ideas while staying inside defined security boundaries. This

Security‑First Learning and Experimentation Culture in Cloud‑Native DevOps Read More »

Security‑First Resilience Patterns in Cloud‑Native DevOps

In many organisations, resilience is treated as a reliability concern (e.g., “we must stay up”), while security is handled as a separate control layer. A security‑first resilience model embeds security into how services handle failures, retries, and recovery, so that a capacity issue or cascading failure cannot become a window for privilege escalation or data‑exposure.

Security‑First Resilience Patterns in Cloud‑Native DevOps Read More »

Security‑First Iteration and Feedback Loops in Cloud‑Native DevOps

In many cloud‑native teams, iteration is driven by velocity and feature completion, while security‑related lessons are scattered across separate postmortems and meetings. A security‑first iteration model builds explicit feedback loops into every sprint: after each release and incident, the team reviews what security issues surfaced, updates golden‑path templates, CI/CD gates, and observability rules, and then

Security‑First Iteration and Feedback Loops in Cloud‑Native DevOps Read More »

Scroll to Top