
Cloud-Native DevOps Security: Shift Security Left for Safer Deployments
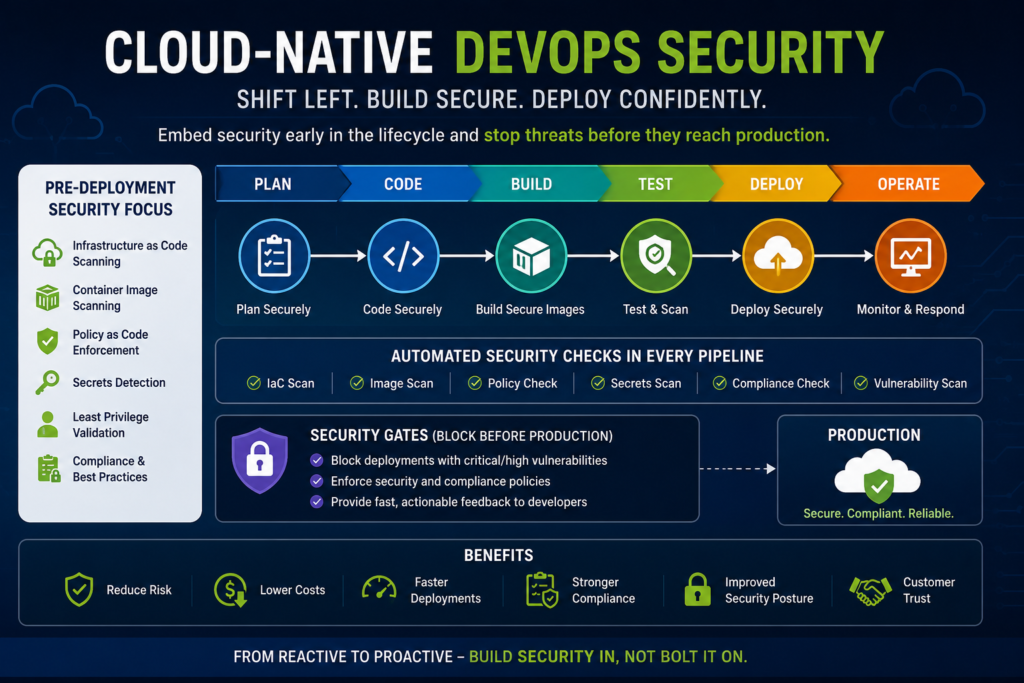
Cloud-native DevOps security is most effective when security is integrated before deployment rather than after production. Fixing vulnerabilities late in the software lifecycle is slow, expensive, and increases business risk. By adopting a shift-left security approach, organizations can detect and resolve security issues early, resulting in faster and more secure software delivery.
Secure Every Stage of the CI/CD Pipeline
A secure DevOps pipeline begins with pre-deployment security checks. Infrastructure-as-Code (IaC) templates, container images, Kubernetes manifests, and application configurations should be scanned automatically during every CI/CD pipeline. Policy-as-Code ensures compliance with organizational security standards, while secret scanning prevents sensitive credentials from being exposed. In addition, least-privilege validation minimizes unnecessary permissions that attackers could exploit.
Implement Automated Security Gates
Automated security gates help prevent vulnerable applications from reaching production. Critical vulnerabilities, insecure configurations, and compliance violations should automatically block deployments until they are resolved. Developers receive fast, actionable feedback, allowing them to fix issues without delaying the software development process.
Build a Shared Security Culture
Successful cloud-native DevOps teams create a shared pre-deployment security contract. Security engineers, platform teams, and developers collaborate to define security baselines that every application must satisfy before release. These baselines are continuously improved using lessons learned from security incidents, audits, and near-miss events.
Benefits of Shift-Left Security
Embedding security into cloud-native DevOps pipelines reduces operational costs, accelerates deployments, improves compliance, and minimizes security risks. Instead of reacting to incidents after production, organizations proactively build secure applications from the beginning. This approach ensures every new service is deployed with a strong security posture, enabling faster innovation while maintaining reliability and customer trust.
🚀 Ready to Transform Your Business?
From AI and Agentic AI to Cloud, Data, Automation, and Digital Transformation, KPSmart IT Solutions helps businesses turn technology opportunities into measurable business outcomes.
Have a challenge? Have an idea? Let’s talk.
👉 Explore KPSmart IT Solutions
KPSmart IT Solutions — Build Smart. Automate. Transform. Grow.
#KPSmartITSolutions #AI #ArtificialIntelligence #AgenticAI #DigitalTransformation #BusinessAutomation #EnterpriseAI #Innovation